Set a user role with SCIM
For setting a different role than the default, please follow the following steps, using Domain Admin as example:
- Ensure the user exists in your Entra ID tenant as per the default process
- Click Cloud Shell in the Azure Portal, see screenshot below, then wait for initialization
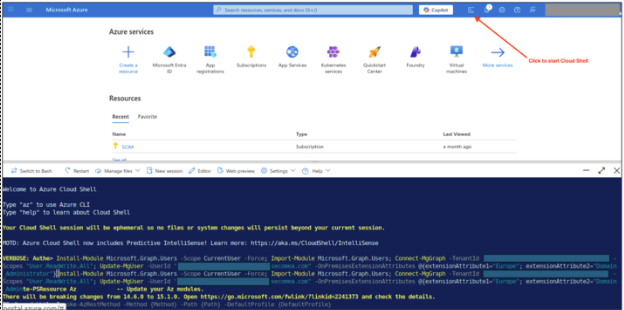
- Add and adapt the script below to the Azure Cloud Shell
Connect-MgGraph -Scopes "User.ReadWrite.All"

# Single user
Update-MgUser -UserId "amundsen@acme.com" -OnPremisesExtensionAttributes @{
ExtensionAttribute1 = "Domain_Administrator" 	# role
}
Where amundsen@acme.com is the UserId of the identity to be assigned the role. Use Basic_Administrator when this is the needed role.
- Execute the script.
- Run Disconnect-MgGraph to close Azure Cloud Shell
- Verify that the user has gotten the role assigned. This can be done via Provision on Demand in Entra, or in Secomea’s system once the user has been provisioned.
For On-Premises synced users, please follow the below approach
Run the following on your Active Directory server or any machine with RSAT AD Tools installed.
Set a Single User
# Import AD module
Import-Module ActiveDirectory

# Set extension attributes
Set-ADUser -Identity "username" -Replace @{
    extensionAttribute1 = "Domain_Administrator"
}

# Verify
Get-ADUser -Identity "username" -Properties extensionAttribute1 |
    Select-Object Name, extensionAttribute1
Set Multiple Users at Once
Import-Module ActiveDirectory
# Define users and their attribute values
$Users = @(
    @{ Username = "user1"; Role = "Domain_Administrator" },
    @{ Username = "user2"; Role = "Basic_Administrator" },
    @{ Username = "user3"; Role = "Basic_Administrator"}
)

foreach ($user in $Users) {
    try {
        Set-ADUser -Identity $user.Username -Replace @{
            extensionAttribute1 = $user.Role
        }
        Write-Host "SUCCESS: $($user.Username) | Role=$($user.Role)" -ForegroundColor Green
    }
    catch {
        Write-Host "FAILED: $($user.Username) | Error: $($_.Exception.Message)" -ForegroundColor Red
    }
}
Force Azure AD Connect Sync
After setting attributes in AD, trigger a sync to push changes to Entra ID.
Run on the Azure AD Connect Server
# Delta sync (syncs only changes — recommended)
Start-ADSyncSyncCycle -PolicyType Delta

# Full sync (syncs everything — use only if delta doesn't work)
Start-ADSyncSyncCycle -PolicyType Initial
Check Sync Status
Get-ADSyncScheduler
Typical sync cycle is 30 minutes. A forced delta sync takes 1-2 minutes.
Verify Sync in Entra ID
After the sync completes, verify the attributes are visible in Entra ID.
Connect-MgGraph -Scopes "User.Read.All"
Invoke-MgGraphRequest -Method GET -Uri "https://graph.microsoft.com/v1.0/users/user@domain.com?`$select=displayName,onPremisesExtensionAttributes"
Expected output:
{
  "displayName": "John Doe",
  "onPremisesExtensionAttributes": {
    "extensionAttribute1": "Domain_Administrator"
  }
}
Final Step - Verify that the user has gotten the role assigned
This can be done via Provision on Demand in Entra, or in Secomea’s system once the user has been provisioned.